The SANS Internet Storm Center operates a global network of honeypots that collectively receive over 10 million connection attempts per day from automated scanning tools, botnets, and human attackers probing for vulnerable systems. Cloudflare’s internal honeypot infrastructure detected and documented 26 novel attack patterns in 2025 before those patterns appeared in production environments, allowing rule updates to block the attacks before they reached real systems. Honeypots have been a core deception technology in cybersecurity since Cliff Stoll famously used a makeshift honeypot to track KGB-linked hackers in 1986, an account documented in his 1989 book “The Cuckoo’s Egg.”
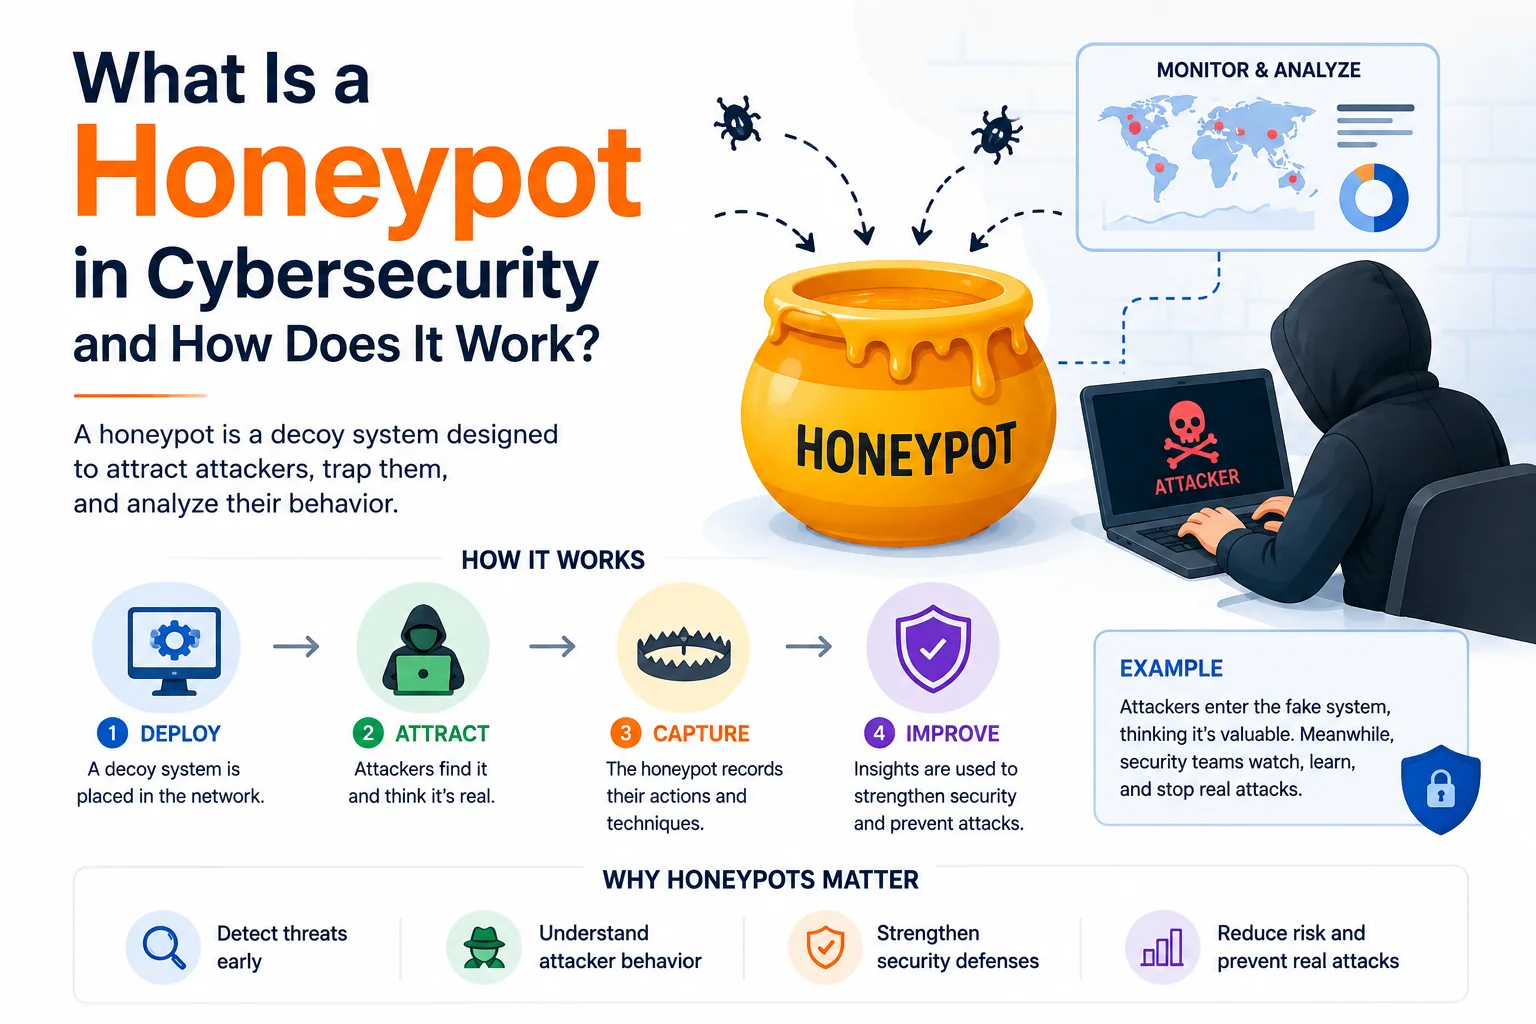
A honeypot is a decoy system, network segment, or resource intentionally made available to attackers to detect, study, or divert their activity. The fundamental principle is deception: the honeypot appears to be a legitimate, valuable target (a server with important files, a database with user credentials, an exposed administrative interface) while containing no real data and producing detailed logging of every action an attacker takes against it. Any interaction with a honeypot is inherently suspicious because legitimate users and systems have no reason to access a resource that serves no production function.
The Types of Honeypots
Honeypots are categorised along two dimensions: deployment purpose (research versus production) and interaction level (low, medium, or high interaction).
Research honeypots are deployed by academic institutions, security firms, and threat intelligence organisations to collect data about attacker techniques, malware behaviour, and emerging attack patterns. The SANS Internet Storm Center’s sensor network is a research honeypot deployment. Research honeypots prioritise data collection over operational security benefit; they are designed to attract and observe attackers comprehensively.
Production honeypots are deployed within real organisational networks to provide early warning of attacks on actual infrastructure. A production honeypot placed in an internal network segment that no legitimate system should ever contact will trigger an alert if any internal device connects to it, which may indicate lateral movement by an attacker who has already compromised an internal endpoint. Production honeypots prioritise alerting and early detection over comprehensive data collection.
Low-interaction honeypots simulate vulnerable services without providing a full operating system environment. They respond to common attack probes (port scans, service banner grabbing, basic authentication attempts) with convincing responses but do not allow attackers to actually execute code or move through the system. They are easier to deploy and maintain but provide limited insight into advanced attacker behaviour. Tools like Dionaea, Honeyd, and Cowrie (for SSH honeypots) implement low-interaction honeypot functionality.
High-interaction honeypots provide a fully functional operating system environment that attackers can genuinely explore, execute code within, and move through. They provide the richest attacker behaviour data but carry higher operational risk (a compromised high-interaction honeypot can be used as an attack staging point) and require more maintenance. High-interaction honeypots are primarily used in research contexts with careful network isolation.
How Honeypots Detect Attackers
The detection logic of honeypots is based on a simple principle: any connection to a honeypot is anomalous by design. Unlike production systems that generate noise from legitimate user activity (making it difficult to distinguish malicious from normal traffic), honeypots have zero legitimate traffic baseline. Every port scan, authentication attempt, and file access request is a detection event.
This is the core advantage honeypots have over signature-based intrusion detection systems (IDS). An IDS must match traffic against known attack signatures, missing novel attacks that have no signature. A honeypot detects any interaction regardless of the attack technique, because there is no legitimate technique for interacting with a system that serves no production purpose.
The detection workflow for a production honeypot deployment typically works as follows: an attacker (or automated scanner) identifies the honeypot as a potential target through network reconnaissance and attempts to connect or authenticate. The honeypot logs the source IP, connection time, protocol used, and any data transmitted. An alert is generated to the security team’s SIEM (Security Information and Event Management) system. If the source IP is internal, this indicates a potentially compromised internal endpoint engaged in lateral movement.
Honeypots vs Honeynets
A honeynet is a network of honeypots working together to simulate an entire organisational network segment with multiple systems. Where a single honeypot simulates one server or service, a honeynet simulates multiple interconnected systems (web server, database server, file server, workstation) that provide a realistic environment for studying how attackers move laterally through a network once they have gained initial access.
The Honeynet Project, a non-profit security research organisation, maintains one of the most extensively documented honeynet deployments globally and has published research on attacker lateral movement patterns, malware families, and command-and-control infrastructure based on honeynet observations.
Honeynets require significantly more infrastructure and expertise to deploy and maintain than individual honeypots, making them primarily a research and enterprise security tool rather than a small business implementation.
Modern Deception Technology
Deception technology platforms, a commercial evolution of honeypot concepts, provide enterprise-scale honeypot deployment and management. Products from Attivo Networks (acquired by SentinelOne in 2022), Illusive Networks, and TrapX Security distribute honeypots and decoy credentials (fake username/password combinations left in configuration files, browser saved passwords, and network shares) across an entire network.
When an attacker who has compromised one endpoint attempts to use these decoy credentials, the use of the credential triggers an immediate alert. This technique, sometimes called credential deception or identity deception, provides detection capability that is effective against attackers who are already inside the network and attempting to escalate privileges or move laterally, which represents the most difficult attacker behaviour category to detect with conventional security controls.
| Honeypot Type | Interaction Level | Best For | Maintenance | Risk Level |
|---|---|---|---|---|
| Low-interaction (Cowrie, Dionaea) | Low | Internal early warning, port scan detection | Low | Low |
| Medium-interaction (custom services) | Medium | Attacker technique sampling | Medium | Medium |
| High-interaction (full OS) | High | Advanced threat research | High | High (isolation required) |
| Honeynet | High | Lateral movement research | Very High | High |
| Commercial deception platform | Medium-High | Enterprise-scale deployment | Managed | Medium |
Setting Up a Basic Honeypot
A basic honeypot for a small business or home lab environment can be deployed in under an hour using open-source tools. Cowrie is the most widely used SSH and Telnet honeypot: it simulates a vulnerable Linux server, logs all commands executed by attackers who successfully authenticate, and captures any files uploaded during the session.
Deployment on a cloud virtual machine (any major cloud provider) at a fresh IP address that has no prior web presence will typically generate initial scanning activity within 24 to 48 hours as automated scanners sweep IP ranges continuously. Reviewing Cowrie logs after 72 hours provides a realistic picture of the attack automation present on the public internet.
For internal network deployment, placing a Raspberry Pi running Cowrie or a similar honeypot on an internal VLAN segment that no legitimate system should contact creates a zero-false-positive early detection system for lateral movement within the organisation.